


Only 31 per cent of banks surveyed in Bangladesh have documented and regularly tested incident response plans for their banking apps, highlighting weaknesses in the sector’s readiness to tackle cyberattacks and customer-facing fraud, a Bangladesh Institute of Bank Management (BIBM) study has found.
The survey found that although 81 per cent of respondents reported having security event logging systems, only 44 per cent monitored application programming interface (API) traffic in real time. The findings point to a gap between recording security events and detecting suspicious activity as it happens.
The study covered 34 banks and examined governance, risk management, secure app development, technical controls, fraud monitoring and customer protection. BIBM cautioned that the findings were based on self-reported practices in a purposive, cross-sectional study and should not be treated as independently audited or representative of the entire banking sector.
Phishing and social engineering were the most frequently reported customer-facing fraud incidents, followed by account takeover and credential theft. Although banks use multiple channels to raise customer awareness, measuring whether those efforts change customer behaviour remains less common.
Authentication systems and oversight of outsourced applications also showed gaps. While 78 per cent of respondents reported using device binding with re-authentication, only 16 per cent had adaptive authentication.
Similarly, 78 per cent operated at least one vendor-developed banking app, but just 34 per cent continuously monitored third-party API security risks.
Resource constraints further limit banks’ preparedness. Budget limitations and inadequate security tools were each cited by 47 per cent of respondents, while 38 per cent reported a shortage of skilled cybersecurity personnel.
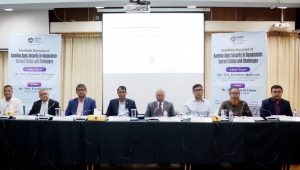
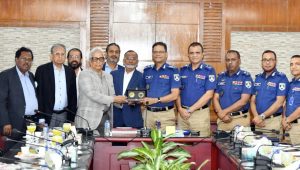
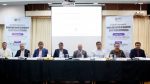
The findings were presented at a BIBM roundtable titled “Banking Apps Security in Bangladesh: Current Status and Challenges” at the institute’s auditorium in Mirpur on Wednesday.
Md Habibur Rahman, deputy governor of Bangladesh Bank and chairman of the BIBM Executive Committee, attended as chief guest. Fahad Ahmed, lecturer at BIBM, presented the keynote paper, prepared with Md Shihab Uddin Khan and Muhammad Abul Kalam Azad, chief information security officer at Eastern Bank.
In his concluding remarks, BIBM Director General Md Ezazul Islam called for joint cybersecurity exercises involving digital banking, fraud operations and customer support teams, stronger verification for high-risk transactions and clearer accountability for third-party technology providers.
He also urged banks to track how quickly they act after customers report suspected fraud and how promptly they address weaknesses identified during security exercises.
The designated discussants included Debdulal Roy, faculty member at BIBM and executive director of Bangladesh Bank, Md Shohrab Hossain of United International University and BUET, and Kazi Azizur Rahman, additional managing director and chief information officer of City Bank.